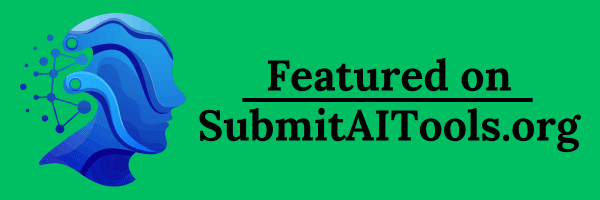
Polylane for Security




Is this your AI tool? Claim it today.
Verify ownership, manage your profile, and unlock growth features.
Polylane leverages AI to provide automated, precise security reviews for every pull request destined for production, uniquely tracing vulnerabilities to attacker inputs to reduce false positives. Ideal for development and security teams seeking seamless, continuous protection and automated fixes within their CI/CD pipelines.
Description
Polylane reviews production-bound pull requests for exploitable security flaws. Findings trace attacker-controlled input to the vulnerable line, with the evidence and suggested fix. Safe candidates are ruled out with a reason. Daily dependency scans find known CVEs, prioritise the most severe and open fix pull requests on active, deployed repositories.
Detailed Description
Polylane is an advanced AI-powered security review tool designed to automatically analyze every pull request that could potentially reach production environments. Its core purpose is to detect and prevent security vulnerabilities early in the software development lifecycle, ensuring that code deployed to production is robust against attacks. By integrating directly into the development workflow, Polylane provides continuous security assurance without requiring manual intervention or slowing down release cycles. It focuses on identifying exploitable flaws such as injection attacks, authentication bypasses, cross-tenant access issues, server-side request forgery (SSRF), cross-site scripting (XSS), embedded secrets in code, and weak cryptographic implementations. This comprehensive detection helps development teams maintain high security standards and reduce the risk of breaches caused by coding errors or vulnerable dependencies. One of Polylane's standout features is its ability to trace each potential vulnerability through the codebase back to an attacker-controlled input. This dynamic tracing significantly reduces false positives by verifying whether a flagged issue is truly exploitable or safely mitigated by validation, escaping, or ownership checks. Unlike traditional static analysis tools that rely solely on pattern matching, Polylane's approach ensures that developers receive actionable and precise security feedback. Additionally, Polylane does not execute code or perform active attacks against endpoints; instead, it analyzes the source code at the head commit of each pull request, preserving safety and compliance. Another key capability is its automated remediation feature, where Polylane opens pull requests to fix vulnerable dependencies, streamlining the patching process and minimizing manual effort. Polylane is best suited for software development teams, security engineers, and DevOps professionals who prioritize secure coding practices and want to embed security checks seamlessly into their CI/CD pipelines. Organizations with complex codebases or those operating in regulated industries can particularly benefit from Polylane’s thorough and automated security reviews. Use cases include early detection of security flaws during code reviews, continuous monitoring of third-party dependencies for vulnerabilities, and reducing the burden on security teams by automating routine fixes. By enabling security reviews by default with options to disable them per workspace or repository, Polylane offers flexibility to accommodate various team workflows and project requirements. Regarding pricing, Polylane offers tiered plans tailored to different organizational sizes and needs, though specific pricing details are typically available upon request or through direct contact with the vendor. This approach allows companies to select plans that align with their scale of operations and security requirements. Potential users are encouraged to reach out to Polylane’s sales or support teams for customized pricing and trial options. Compared to alternative security review tools, Polylane distinguishes itself with its AI-driven vulnerability tracing and automated dependency fixes. Many competitors rely on static pattern matching or require manual triage of alerts, which can lead to alert fatigue and missed issues. Polylane’s focus on reducing false positives and automating remediation accelerates secure software delivery. However, some limitations to consider include the necessity of integrating Polylane into existing development workflows, which may require initial setup effort, and the dependency on source code availability for analysis. Also, while Polylane covers a broad range of vulnerabilities, organizations should complement it with runtime security tools and penetration testing for comprehensive protection. In summary, Polylane offers a powerful, AI-enhanced security review solution that helps development teams detect, verify, and fix security vulnerabilities early and efficiently. Its unique combination of code tracing, automated fixes, and seamless integration makes it a valuable asset for teams aiming to deliver secure software at speed. Prospective users should evaluate their specific security needs and integration capabilities to maximize the benefits of Polylane within their development lifecycle.
Tool Features
- Checks every pull request that reaches production for security flaws
- Detects vulnerabilities like injection, authentication bypass, SSRF, XSS, secrets in code, and weak cryptography
- Traces each candidate vulnerability to an attacker-controlled input to reduce false positives
- Automatically fixes vulnerable dependencies by opening pull requests
- Does not run code or attack endpoints; analyzes source code at pull request head commit
- Security reviews are enabled by default with options to disable per workspace or repository
Description
Polylane leverages AI to provide automated, precise security reviews for every pull request destined for production, uniquely tracing vulnerabilities to attacker inputs to reduce false positives. Ideal for development and security teams seeking seamless, continuous protection and automated fixes within their CI/CD pipelines.
Polylane reviews production-bound pull requests for exploitable security flaws. Findings trace attacker-controlled input to the vulnerable line, with the evidence and suggested fix. Safe candidates are ruled out with a reason. Daily dependency scans find known CVEs, prioritise the most severe and open fix pull requests on active, deployed repositories.
Detailed Description
Polylane is an advanced AI-powered security review tool designed to automatically analyze every pull request that could potentially reach production environments. Its core purpose is to detect and prevent security vulnerabilities early in the software development lifecycle, ensuring that code deployed to production is robust against attacks. By integrating directly into the development workflow, Polylane provides continuous security assurance without requiring manual intervention or slowing down release cycles. It focuses on identifying exploitable flaws such as injection attacks, authentication bypasses, cross-tenant access issues, server-side request forgery (SSRF), cross-site scripting (XSS), embedded secrets in code, and weak cryptographic implementations. This comprehensive detection helps development teams maintain high security standards and reduce the risk of breaches caused by coding errors or vulnerable dependencies. One of Polylane's standout features is its ability to trace each potential vulnerability through the codebase back to an attacker-controlled input. This dynamic tracing significantly reduces false positives by verifying whether a flagged issue is truly exploitable or safely mitigated by validation, escaping, or ownership checks. Unlike traditional static analysis tools that rely solely on pattern matching, Polylane's approach ensures that developers receive actionable and precise security feedback. Additionally, Polylane does not execute code or perform active attacks against endpoints; instead, it analyzes the source code at the head commit of each pull request, preserving safety and compliance. Another key capability is its automated remediation feature, where Polylane opens pull requests to fix vulnerable dependencies, streamlining the patching process and minimizing manual effort. Polylane is best suited for software development teams, security engineers, and DevOps professionals who prioritize secure coding practices and want to embed security checks seamlessly into their CI/CD pipelines. Organizations with complex codebases or those operating in regulated industries can particularly benefit from Polylane’s thorough and automated security reviews. Use cases include early detection of security flaws during code reviews, continuous monitoring of third-party dependencies for vulnerabilities, and reducing the burden on security teams by automating routine fixes. By enabling security reviews by default with options to disable them per workspace or repository, Polylane offers flexibility to accommodate various team workflows and project requirements. Regarding pricing, Polylane offers tiered plans tailored to different organizational sizes and needs, though specific pricing details are typically available upon request or through direct contact with the vendor. This approach allows companies to select plans that align with their scale of operations and security requirements. Potential users are encouraged to reach out to Polylane’s sales or support teams for customized pricing and trial options. Compared to alternative security review tools, Polylane distinguishes itself with its AI-driven vulnerability tracing and automated dependency fixes. Many competitors rely on static pattern matching or require manual triage of alerts, which can lead to alert fatigue and missed issues. Polylane’s focus on reducing false positives and automating remediation accelerates secure software delivery. However, some limitations to consider include the necessity of integrating Polylane into existing development workflows, which may require initial setup effort, and the dependency on source code availability for analysis. Also, while Polylane covers a broad range of vulnerabilities, organizations should complement it with runtime security tools and penetration testing for comprehensive protection. In summary, Polylane offers a powerful, AI-enhanced security review solution that helps development teams detect, verify, and fix security vulnerabilities early and efficiently. Its unique combination of code tracing, automated fixes, and seamless integration makes it a valuable asset for teams aiming to deliver secure software at speed. Prospective users should evaluate their specific security needs and integration capabilities to maximize the benefits of Polylane within their development lifecycle.
Frequently Asked Questions
What is Polylane?
Polylane is an AI-powered security review tool that analyzes every pull request capable of reaching production to detect security vulnerabilities such as injection flaws, authentication bypasses, SSRF, XSS, secrets in code, and weak cryptography. It traces vulnerabilities through code to confirm exploitability and automatically fixes vulnerable dependencies by opening pull requests.
How much does Polylane cost?
Polylane offers tiered pricing plans tailored to different organizational needs and sizes. Specific pricing details are typically provided upon request or through direct contact with Polylane's sales team to ensure the best fit for your requirements.
Who is Polylane best for?
Polylane is best suited for software development teams, security engineers, and DevOps professionals who want to integrate continuous, automated security reviews into their development workflows. It is especially beneficial for organizations with complex codebases or those in regulated industries requiring rigorous security standards.
What are the main features of Polylane?
Key features include AI-powered detection of security flaws in every pull request, tracing vulnerabilities to attacker-controlled inputs to reduce false positives, automated fixing of vulnerable dependencies via pull requests, source code analysis without running code or attacking endpoints, and default-enabled security reviews with options to disable per workspace or repository.
Does Polylane offer a free trial?
Information about free trials is not explicitly stated publicly. Interested users should contact Polylane directly to inquire about trial availability or demo options.
What integrations does Polylane support?
Polylane integrates into development workflows by analyzing pull requests at their head commit, making it compatible with common version control and CI/CD systems. Specific integrations are not detailed publicly, so contacting Polylane for precise integration capabilities is recommended.
How does Polylane work?
Polylane works by analyzing the source code of pull requests before they reach production, using AI to detect potential security vulnerabilities. It traces each flagged issue back to attacker-controlled inputs to confirm exploitability, reducing false positives. It also automatically opens pull requests to fix vulnerable dependencies, helping maintain secure codebases efficiently.
Socials

Reviews
No reviews yet. Be the first to share your experience.