🚀 Zaprep: je socials on steroids. Start gratis — automatiseer 1.000 DM's/maand en zet engagement om in leads. met 1.000 geautomatiseerde DM's/maand.
Dien je tool in
PoweredByAI.app is een AI-toolsdirectory die individuen, bedrijven en creators helpt de beste AI-tools te ontdekken voor schrijven, coderen, design, productiviteit en meer.
© 2026 , Een product van011BQ. Alle rechten voorbehouden.

Ananonymous Substack postpublished this week accuses compliance startupDelveof “falsely” convincing “hundreds of customers they were compliant” with privacy and security regulations, potentially exposing those customers to “criminal liability under HIPAA and hefty fines under GDPR.” Delve is a Y Combinator-backed startup that last yearannounced raising a $32 million Series Aat a $300 million valuation. (The round was led by Insight Partners.) On Friday, the startup attempted to refute the accusationson its blog, calling the Substack post “misleading” and saying it “contains a number of inaccurate claims.” The Substack post is credited to “DeepDelver,” who described themselves as working at a (now former) Delve client. In response to emailed questions from TechCrunch, DeepDelver said that they and their collaborators “chose to remain anonymous out of fear for retaliation by Delve.” In their post, DeepDelver recounted receiving an email in December claiming the startup had “leaked a spreadsheet with confidential client reports.” While Delve CEO Karun Kaushik apparently assured customers in a subsequent email that they were in compliance and that no external party gained access to sensitive data, DeepDelver said they and other customers had become suspicious. “Having the shared experience of being underwhelmed with the Delve experience, and having the overall sense that something fishy was going on, we decided to pool resources and investigate together,” they wrote. Their conclusion? That Delve “achieves its claim of being the fastest platform by producing fake evidence, generating auditor conclusions on behalf of certification mills that rubber stamp reports, and skipping major framework requirements while telling clients they have achieved 100% compliance.” DeepDelver went into considerable detail about those claims, accusing the startup of providing customers with “fabricated evidence of board meetings, tests, and processes that never happened,” then forcing those customers to “choose between adopting fake evidence or performing mostly manual work with little real automation or AI.” DeepDelver also claimed that virtually all of Delve’s clients seem to have gone through two audit firms, Accorp and Gradient, which they described as “part of the same operation,” one that operates primarily in India, with only a nominal presence in the United States. Those firms, they said, are just rubber-stamping reports that were generated by Delve. As a result, DeepDelver said the startup “inverts” the normal compliance structure: “By generating auditor conclusions, test procedures, and final reports before any independent review occurs, Delve places itself in the role of both implementer and examiner. This is not a technicality. It is a structural fraud that invalidates the entire attestation.” In addition to accusing Delve of misleading its customers, DeepDelver said the startup is helping those customers “mislead the public by hosting trust pages that contain security measures that were never implemented.” DeepDelver said that while their company was discussing its issues with Delve, the startup “sent us multiple boxes of donuts […] to keep us happy.” Nonetheless, DeepDelver’s employer supposedly unpublished its trust page and no longer relies on the startup for compliance. Delve responded to the accusations by saying it does not issue compliance reports at all. Instead, it’s an “automation platform” that ingests information about compliance, then provides auditors with access to that information. “Final reports and opinions are issued solely by independent, licensed auditors, not Delve,” the company said. Delve also said that its customers “can opt to work with an auditor of their choosing or opt to work with one from Delve’s network of independent, accredited third-party audit firms.” Those auditors, the startup said, are “established firms used broadly across the industry, including by other compliance platforms.” In response to the accusation that it’s providing customers with “fake evidence,” Delve countered that it’s simply offering “templates to help teams document their processes in accordance with compliance requirements, as do other compliance platforms.” “Draft templates are not the same as ‘pre-filled evidence,’” the company said. Delve added that it is “actively investigating any leaks” and is “still reviewing the Substack.” When asked about Delve’s response, DeepDelver told TechCrunch that they were “baffled by the laziness, clumsiness and brazenness of it.” “They are trying to snake their way out [of] being held accountable by denying having ‘pre-filled evidence’ but calling it ‘templates’ instead, effectively shifting the blame to customers for adopting the ‘templates’ as is,” DeepDelver said. “They’re claiming they are not the ones to ‘issue’ the report, which is easy to claim if you define issuing a report as providing the final stamp.” They added that there are “a number of very serious allegations” that Delve did not address at all: “The India accusation, the lack of AI (they only talk about ‘automations’), and the trust (lol) page containing controls that were never implemented.” Apparently DeepDelver isn’t done with its criticism, as it promised, “Part II will follow soon.” In addition, following the initial Substack post, an X user named James Zhousaidthey were able to gain access to sensitive information from Delve, such as employee background checks and equity vesting schedules. Dvuln founder Jamieson O’Reillyshared more detailsfrom what O’Reilly said was a conversation with Zhou about “several gaping security holes in Delve’s external attack surface.” TechCrunch sent an email seeking additional comment to the media contact address listed on Delve’s website. The email bounced, but after this article was published, I received a calendar invite for a “Delve demo” later this week. This post was initially published on March 21, 2026. It has been updated with emailed answers from DeepDelver, additional information about purported security vulnerabilities provided by Jamieson O’Reilly, and additional details about Delve’s response to TechCrunch.
View

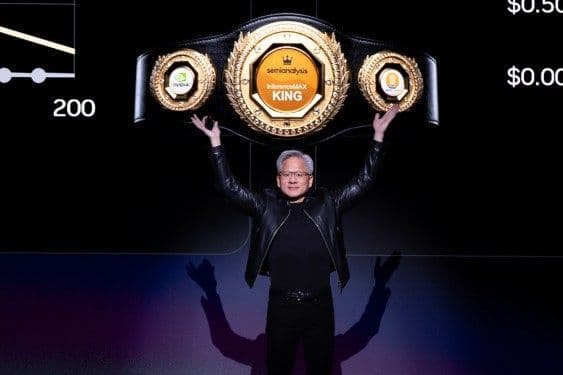
This week, a topic that has been boomeranging around Silicon Valley bounced into the spotlight: AI tokens as compensation. The idea is straightforward enough — rather than giving engineers only salary, equity, and bonuses, companies would also hand them a budget of AI tokens, the computational units that power tools like Claude, ChatGPT, and Gemini. Spend them to run agents, automate tasks, crank through code. The pitch is that access to more compute makes engineers more productive, and that more productive engineers are worth more. It’s an investment in the person holding them, is the idea. Jensen Huang, the leather-jacket-wearing CEO of Nvidia, seemed to capture everyone’s imagination when he floated the notion at the company’s annual GTC event earlier this week that engineers should receive roughly half their base salary again — in tokens. His top people, by his math, might burn through$250,000 a yearin AI compute. He called it a recruiting tool and predicted it would become standard across Silicon Valley. It isn’t entirely clear where the idea was first, well, ideated. Tomasz Tunguz, a renowned VC in the Bay Area who runs Theory Ventures and focuses on AI, data, and SaaS startups — and whose writing on all things data has garnered a loyal following over the years — was talking about this in mid-February, writing that tech startups were already adding inference costs as a “fourth componentto engineering compensation.” Using data from the compensation tracking site Levels.fyi, he put a top-quartile software engineer salary at $375,000. Add $100,000 in tokens and you’re at $475,000 fully loaded — meaning roughly one dollar in five is now compute. That’s no coincidence. Agentic AI has been taking off, and therelease of OpenClawin late January accelerated the conversation considerably. OpenClaw is an open-source AI assistant designed to run continuously — churning through tasks, spawning sub-agents, and working through a to-do list while its user sleeps. It’s part of a broader shift toward “agentic” AI, meaning systems that don’t just respond to prompts but take sequences of actions autonomously over time. The practical consequence is that token consumption has exploded. Where someone writing an essay might use 10,000 tokens in an afternoon, an engineer running a swarm of agents can blow through millions in a day — automatically, in the background, without typing a word. By this weekend, the New York Times had put together asmart lookat the so-called tokenmaxxing trend, finding that engineers at companies including Meta and OpenAI are competing on internal leaderboards that track token consumption. Generous token budgets are quietly becoming a standard job perk, the paper reported, the way dental insurance or free lunch once was. One Ericsson engineer in Stockholm told the Times he probably spends more on Claude than he earns in salary, though his employer picks up the tab. Maybe tokens really will become the fourth pillar of engineering compensation. But engineers might want to hold the line before embracing this as a straightforward win. More tokens may mean more power in the short term, but given how fast things are evolving, it doesn’t necessarily mean more job security. For one thing, a large token allotment comes with large expectations. If a company is effectively funding a second engineer’s worth of compute on your behalf, the implicit pressure is to produce at twice the rate (or more). And there’s a muddier problem underneath that: at the point where a company’s token spend per employee approaches or exceeds that employee’s salary, the financial logic of headcount starts to look different to its finance team. If the compute is doing the work, the question of how many humans need to be coordinating it becomes harder to avoid. Jamaal Glenn, an East Coast-based Stanford MBA and former VC turned financial services CFO, similarlypoints outthat what may seem like a perk can be a clever way for companies to inflate the apparent value of a compensation package without increasing cash or equity — the things that actually compound for an employee over time. Your token budget doesn’t vest. It doesn’t appreciate. It doesn’t show up in your next offer negotiation the way a base salary or equity grant does. If companies successfully normalize tokens as pay, they may find it easier to keep cash comp flat while pointing to a growing compute allowance as evidence of investment in their people. That’s a good deal for the company. Whether it’s a good deal for the engineer depends on questions most engineers don’t yet have enough information to answer.

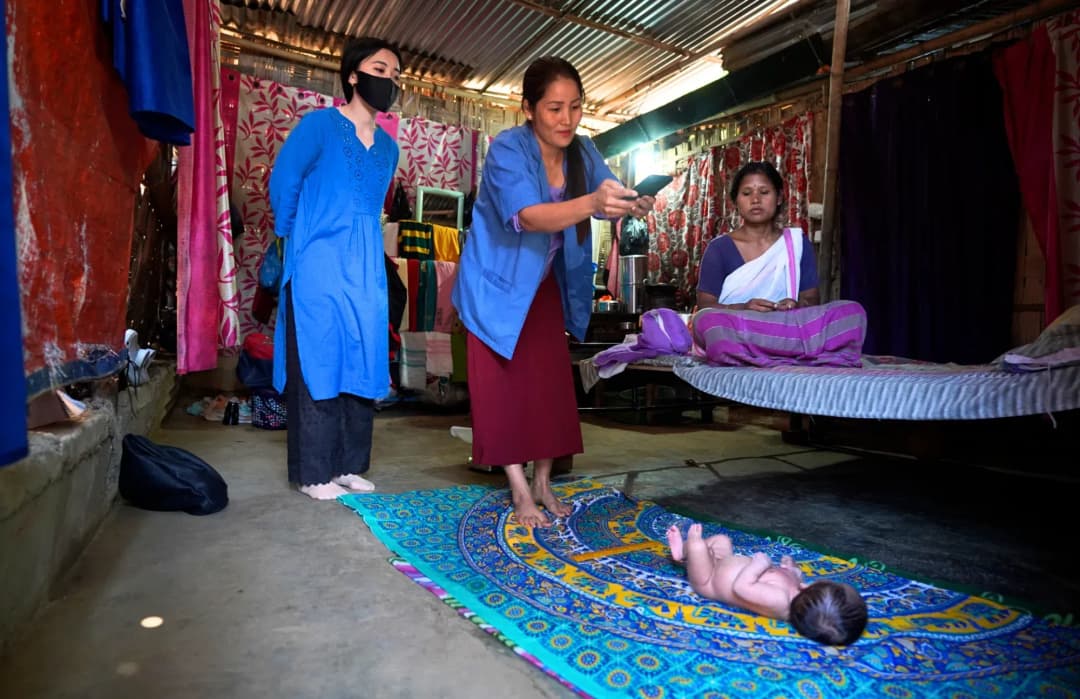
Developed by Wadhwani AI, Shishu Mapaan uses video and AI to estimate anthropometric metrics of newborns, enabling faster, more accessible frontline care.
View

When Nvidia CEO Jensen Huang took the stage for hisannual GTC keynoteon Monday, the $4-trillion-dollar company’s stock started to drop. Wall Street investors, it seems, were unmoved by the leather jacket-clad founder’s bullish 2.5-hour speech. Instead, they placed more weight on AI’s uncertain future and fears of a bubble. The nervousness felt by Wall Street couldn’t be more different than the buzzy atmosphere in Silicon Valley, where confidence, not uncertainty abounds. Huang talked for more than two hours about the company’s latest innovations, from newvideo game graphics techandupdated networking infrastructureto autonomous vehicle deals and a new chip designed with Groq to accelerate AI inference in the Vera Rubin system. He also threw out some eye-watering numbers about Nvidia’s business and beyond. Huang called the AI agent ecosystem a $35 trillion market and the physical AI and robotics industry a $50 trillion market. Huang also said he expects to see$1 trillion worth of purchase ordersfor the company’s Blackwell and Vera Rubin chips — just two of Nvidia’s many products — by the end of 2027. Shouldn’t that make investors excited? It’s not surprising that they aren’t, Futurum CEO Daniel Neuman told TechCrunch. “[AI] is so good, so transformational, and moving so fast that we don’t actually understand what it’s going to mean for all the things that are the societal constructs that we’ve come to understand,” Neuman said. “The markets hate uncertainty. The speed of innovation has actually created a great new uncertainty that I think most people never expected.” Some of that uncertainty comes from misleading information coming out of the market, Neuman said, who added that headlines about low enterprise adoption of AI aren’t painting the full picture — at least, based on conversations he’s having. “Enterprise AI adoption is going to hit inflection and scale very quickly,” Neuman said. “I actually think it’s happening. When you say it’s not, I think what you’re probably saying is the [return on investment] and the receipts are still a little bit undefined and companies are citing the surveys and the reports that are largely six-month-old data. It just takes months to aggregate data.” This sentiment holds weight when you look at Nvidia’s numbers from past quarters. While companies may not be touting their AI ROI, they are increasingly purchasing Nvidia’s tech. The company continues to not only beat its lofty goals and quarterly estimates, but soar past them. Nvidia’s revenue was up 73% year-over-year last quarter. There is no sign that will change any time soon either. For example, just this week Nvidia confirmed Amazon made a plan to purchase 1 million GPUs, alongside other AI infrastructure, by the end of 2027 for Amazon Web Services (AWS),according to reporting from Reuters. Kevin Cook, a senior equity strategist at Zacks Investment Research, agreed with Neuman and joked to TechCrunch that investors not being happy doesn’t change the fact that the whole stock market is propped up by Nvidia, because its tech runs the rails for many of these businesses. “The economy is sort of orbiting around Nvidia,” Cook said. “It’s building this necessary infrastructure. All these different companies in hardware and software and physical AI — even Caterpillar is now physical AI — that are building off of these platforms.” None of this means there isn’t currently an AI bubble or couldn’t be one in the future. But while GTC may not have been a boon for Nvidia’s stock, the broader uncertainty doesn’t seem to be Nvidia’s problem. The company is clearly barreling full steam ahead, bringing seemingly the entire global economy right alongside it. “Nvidia, as you know, is a platform company,” Huang said in his GTC keynote. “We have technology. We have our platforms. We have a rich ecosystem, and today there are probably 100% of the $100 trillion dollars of industry here.

Ananonymous Substack postpublished this week accuses compliance startupDelveof “falsely” convincing “hundreds of customers they were compliant” with privacy and security regulations, potentially exposing those customers to “criminal liability under HIPAA and hefty fines under GDPR.” Delve is a Y Combinator-backed startup that last yearannounced raising a $32 million Series Aat a $300 million valuation. (The round was led by Insight Partners.) On Friday, the startup attempted to refute the accusationson its blog, calling the Substack post “misleading” and saying it “contains a number of inaccurate claims.” The Substack post is credited to “DeepDelver,” who described themselves as working at a (now former) Delve client. DeepDelver recounted receiving an email in December claiming the startup had “leaked a spreadsheet with confidential client reports.” While Delve CEO Karun Kaushik apparently assured customers in a subsequent email that they were in compliance and that no external party gained access to sensitive data, DeepDelver said they and other customers had become suspicious. “Having the shared experience of being underwhelmed with the Delve experience, and having the overall sense that something fishy was going on, we decided to pool resources and investigate together,” they wrote. Their conclusion? That Delve “achieves its claim of being the fastest platform by producing fake evidence, generating auditor conclusions on behalf of certification mills that rubber stamp reports, and skipping major framework requirements while telling clients they have achieved 100% compliance.” DeepDelver went into considerable detail about those claims, accusing the startup of providing customers with “fabricated evidence of board meetings, tests, and processes that never happened,” then forcing those customers to “choose between adopting fake evidence or performing mostly manual work with little real automation or AI.” DeepDelver also claimed that virtually all of Delve’s clients seem to have gone through two audit firms, Accorp and Gradient, which they described as “part of the same operation,” one that operates primarily in India, with only a nominal presence in the United States. Those firms, they said, are just rubber-stamping reports that were generated by Delve. As a result, DeepDelver said the startup “inverts” the normal compliance structure: “By generating auditor conclusions, test procedures, and final reports before any independent review occurs, Delve places itself in the role of both implementer and examiner. This is not a technicality. It is a structural fraud that invalidates the entire attestation.” In addition to accusing Delve of misleading its customers, DeepDelver said the startup is helping those customers “mislead the public by hosting trust pages that contain security measures that were never implemented.” DeepDelver said that while their company was discussing its issues with Delve, the startup “sent us multiple boxes of donuts already to keep us happy.” Nonetheless, DeepDelver’s employer supposedly unpublished its trust page and no longer relies on the startup for compliance. Delve responded to the accusations by saying it does not issue compliance reports at all. Instead, it’s an “automation platform” that ingests information about compliance, then provides auditors with access to that information. “Final reports and opinions are issued solely by independent, licensed auditors, not Delve,” the company said. Delve also said that its customers “can opt to work with an auditor of their choosing or opt to work with one from Delve’s network of independent, accredited third-party audit firms.” Those auditors, the startup said, are “established firms used broadly across the industry, including by other compliance platforms.” In response to the accusation that it’s providing customers with “fake evidence,” Delve countered that it’s simply offering “templates to help teams document their processes in accordance with compliance requirements, as do other compliance platforms.” “Draft templates are not the same as ‘pre-filled evidence,” the company said. Delve added that it is “actively investigating any leaks” and is “still reviewing the Substack.” Following the initial Substack post, an X user named James Zhousaidthey were able to gain access to sensitive information from Delve, such as employee background checks and equity vesting schedules. Dvuln founder Jamieson O’Reillyshared more detailsfrom what O’Reilly said was a conversation with Zhou about “several gaping security holes in Delve’s external attack surface.” TechCrunch sent an email seeking additional comment to the media contact address listed on Delve’s website. The email bounced, but I subsequently received a calendar invite for a “Delve demo” later this week. TechCrunch has also reached out to DeepDelver for additional comment. This post has been updated with additional information about purported security vulnerabilities provided by Jamieson O’Reilly, and additional details about Delve’s response to TechCrunch.

Hachette Book Group said it will not be publishing a novel called “Shy Girl” over concerns that artificial intelligence was used to generate the text. The novel was scheduled to be published in the United States this spring. Hachette said it will also discontinue the book in the United Kingdom, where it’s already available. Although the publisher claimed the decision came after a thorough review of the text, reviewers onGoodReadsandYouTubehad been speculating that the book was likely AI-generated. AndThe New York Times saidit asked Hachette about the “Shy Girl” concerns the day before the announcement. In an email to the NYT, author Mia Ballard denied using AI to write her novel, instead blaming an acquaintance she’d hired to edit the original, self-published version of “Shy Girl.” Ballard said she’s pursuing legal action, and that as a result of the controversy “my mental health is at an all time low and my name is ruined for something I didn’t even personally do.” Writer Lincoln Michel and other industry observers have noted that U.S. publishersrarely do extensive editingwhen they acquire titles that have already been published in other forms.
View

Cursor accesses the Kimi K2.5 model through Fireworks AI, which provides hosted inference and reinforcement learning infrastructure.
View

Anthropic submitted two sworn declarations to a California federal court late Friday afternoon, pushing back on the Pentagon’s assertion that the AI company poses an “unacceptable risk to national security” and arguing that the government’s case relies on technical misunderstandings and claims that were never actually raised during the months of negotiations that preceded the dispute. The declarations were filed alongside Anthropic’s reply brief in its lawsuit against the Department of Defense and come ahead of a hearing this coming Tuesday, March 24, before Judge Rita Lin in San Francisco. The dispute traces back to late February, when President Trump and Defense Secretary Pete Hegseth publicly declared they were cutting ties with Anthropic after the company refused to allow unrestricted military use of its AI technology. The two people who submitted the declarations are Sarah Heck, Anthropic’s Head of Policy, and Thiyagu Ramasamy, the company’s Head of Public Sector. Heck is a former National Security Council official who worked at the White House under the Obama administration before moving to Stripe and then Anthropic, where she runs the company’s government relationships and policy work. She was personally present at the February 24 meeting where CEO Dario Amodei sat down with Defense Secretary Hegseth and the Pentagon’s Under Secretary Emil Michael. In herdeclaration, Heck calls out what she describes as a central falsehood in the government’s filings: that Anthropic demanded some kind of approval role over military operations. That claim, she says, simply isn’t true. “At no time during Anthropic’s negotiations with the Department did I or any other Anthropic employee state that the company wanted that kind of role,” she wrote. She also claims that the Pentagon’s concern about Anthropic potentially disabling or altering its technology mid-operation was never raised during negotiations. Instead, she says, it appeared for the first time in the government’s court filings, which gave Anthropic no opportunity to respond. Another detail in Heck’s declaration sure to draw attention is that on March 4 — the day after the Pentagon formally finalized its supply-chain risk designation against Anthropic — Under Secretary Michael emailed Amodei to say the two sides were “very close” on the two issues the government now cites as evidence that Anthropic is a national security threat: its positions on autonomous weapons and mass surveillance of Americans. The email, which Heck attaches as an exhibit to her declaration, is worth reading alongside what Michael said publicly in the days afterward. On March 5, Amodei published a statement saying the company had been having “productive conversations” with the Pentagon. The day after that, Michaelposted on Xthat “there is no active Department of War negotiation with Anthropic.” A week after that, he told CNBC there was “no chance” of renewed talks. Heck’s point appears to be: If Anthropic’s stance on those two issues is what makes it a national security threat, why was the Pentagon’s own official saying the two sides were nearly aligned on exactly those issues right after the designation was finalized? (She stops short of saying the government used the designation as a bargaining chip, but the timeline she lays out leaves the question hanging.) Ramasamy brings a different kind of expertise to the case. Before joining Anthropic in 2025, he spent six years at Amazon Web Services managing AI deployments for government customers, including classified environments. At Anthropic, he’s credited with building the team that brought its Claude models into national security and defense settings, including the$200 million contractwith the Pentagon announced last summer. Hisdeclarationtakes on the government’s claim that Anthropic could theoretically interfere with military operations by disabling the technology or otherwise altering how it behaves, which Ramasamy says isn’t technically possible. Per his telling, once Claude is deployed inside a government-secured, “air-gapped” system operated by a third-party contractor, Anthropic has no access to it; there is no remote kill switch, no backdoor, and no mechanism to push unauthorized updates. Any kind of “operational veto” is a fiction, he suggests, explaining that a change to the model would require the Pentagon’s explicit approval and action to install. Anthropic, he says, can’t even see what government users are typing into the system, let alone extract that data. Ramasamy also disputes the government’s claim that Anthropic’s hiring of foreign nationals makes the company a security risk. He notes that Anthropic employees have undergone U.S. government security clearance vetting — the same background check process required for access to classified information — adding in his declaration that “to my knowledge,” Anthropic is the only AI company where cleared personnel actually built the AI models designed to run in classified environments. Anthropic’s lawsuit argues that the supply-chain risk designation — the first ever applied to an American company — amounts to government retaliation for the company’s publicly stated views on AI safety, in violation of the First Amendment. The government, in a 40-page filing earlier this week,rejected that framing entirely, saying that Anthropic’s refusal to allow all lawful military uses of its technology was a business decision, not protected speech, and that the designation was a straightforward national security call and not punishment for the company’s views.

Celestial Aerospace targets a commercial orbital launch by early 2029. Shreyans Jain says the next few years will test the team’s pace and discipline.
View

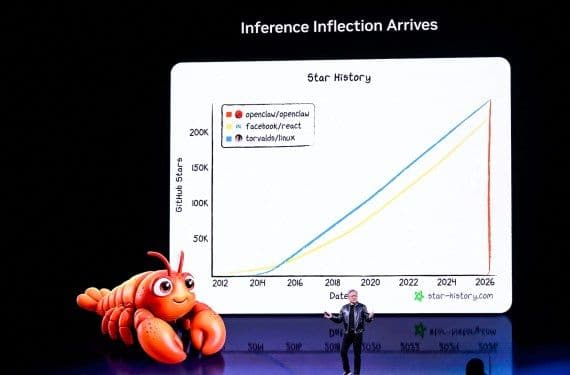
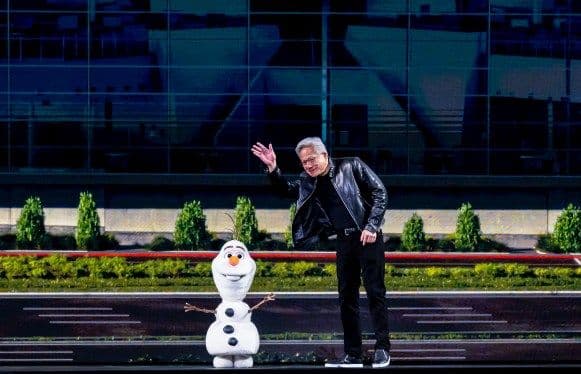
CEO Jensen Huang took the stage atNvidia’s GTC conferencethis week in his signature leather jacket to deliver a two-and-a-half-hour keynote, projecting $1 trillion in AI chip sales through 2027, declaring that every company needs an “OpenClaw strategy,” and closing with a rambling Olaf robot that had to get its mic cut. The message was hard to miss: Nvidia wants to be foundational to everything, from AI training to autonomous vehicles to Disney parks. On this episode of TechCrunch’sEquitypodcast, Kirsten Korosec, Anthony Ha, and Sean O’Kane break down what Nvidia’s growing web of AI infrastructure partnerships actually means for startups, and discuss more of the week’s headlines. Listen to the full episode to hear about: Subscribe to Equity onYouTube,Apple Podcasts,Overcast,Spotifyand all the casts. You also can follow Equity onXandThreads, at @EquityPod.
View

Loading the player… CEO Jensen Huang took the stage atNvidia’s GTC conferencethis week in his signature leather jacket to deliver a two-and-a-half-hour keynote, projecting $1 trillion in AI chip sales through 2027, declaring that every company needs an “OpenClaw strategy,” and closing with a rambling Olaf robot that had to get its mic cut. The message was hard to miss: Nvidia wants to be foundational to everything, from AI training to autonomous vehicles to Disney parks. On this episode of TechCrunch’sEquitypodcast, Kirsten Korosec, Anthony Ha, and Sean O’Kane break down what Nvidia’s growing web of AI infrastructure partnerships actually means for startups, and discuss more of the week’s headlines. Subscribe to Equity onYouTube,Apple Podcasts,Overcast,Spotifyand all the casts. You also can follow Equity onXandThreads, at @EquityPod.
View

Microsoftannouncedon Friday a series of changes focused on improving the quality of its Windows 11 operating system, which notably includes dialing back the number of entry points to its AI assistant, Copilot. The company said it will reduce Copilot AI integrations in some apps, starting with Photos, Widgets, Notepad, and its Snipping Tool. Under the heading of “integrating AI where it’s most meaningful,”Pavan Davuluri, EVP of Windows and Devices, wrote on the company’s blog that Microsoft is becoming more intentional about “how and where Copilot integrates across Windows.” Its goal, he explained, is to focus on AI experiences that are “genuinely useful.” This “less-is-more” approach to integrating AI into existing platforms may reflect the growing consumer pushback against AI bloat. While many people today understand AI to be a useful tool, there are also concerns around trust and safety. For instance, aPew Research studypublished this month noted that half of U.S. adults are now more concerned than excited about AI as of June 2025, up from 37% in 2021. This is not the first time Microsoft has rethought its Copilot integrations. Earlier this month, the news siteWindows Centralsaid the company’s plan to ship Copilot-branded AI features across Windows 11 had been quietly shelved. This, the site said, included some system-level integrations within the Settings app, File Explorer, and elsewhere. Before this, Microsoft haddelayed the launchof its AI-powered memory feature, Windows Recall for Copilot + PCs, for over a year as it tried to address users’ privacy concerns. The Recall feature launched last April, but security vulnerabilities arestill being discovered. It’s clear that user feedback is influencing Microsoft’s moves around AI on Windows. Davuluri wrote that he and his team have spent the past several months listening to the community about how they’d like to see Windows improved. The Copilot rollback is just one of the changes being made. The company said it’s also introducing the ability to move the taskbar to the top or sides of the screen, giving users more control over system updates, speeding up File Explorer, improving the Widgets experience, updating the Feedback Hub, and making it easier to navigate its Windows Insider Program — a community that offers feedback about Windows’ future.
View
View
View
View
View